Picking the data center where your business-critical data will live is not easy.
Many factors shape that choice. Data center location is one of the biggest. Where your colocation site sits affects latency, security, and compliance. It also decides how good your network access is and how much regional risk you take on. Location even sets how well you protect your data physically, logically, and operationally.
Whether you need colocation for a primary or secondary site, the same factors apply. The facility will house your hardware, software, and valuable data, so it must be reliable, redundant, secure, and well powered.
Managing data in-house can get complex and costly. VPNs, remote access, and monitoring help, but servers are physical machines. They need professional human attention when something goes wrong. So data center location matters here too.
This blog explains how data center location impacts performance and security. It also gives practical guidance on choosing a facility that fits your organization’s needs.
Understanding Data Center Location and the Link to Performance and Security
Data center location determines how fast data travels between users and applications. It also affects how safe your data is from attacks and regional disruptions, and it shapes your compliance choices. In fact, location determines how operationally and technically successful colocation can be.
Latency Concerns
Because physical distance directly affects how long data takes to reach the user, data center location directly impacts application speed. Signals move close to the speed of light through fiber. Even so, every extra mile adds measurable delay. That delay matters for latency-sensitive workloads like VoIP, online gaming, and financial transactions. Real-time collaboration tools and interactive web applications feel it too. In these cases, even milliseconds matter.
Placing infrastructure closer to your primary users reduces data round-trip times and improves response times. Proximity to major carrier hotels, internet exchanges, and cloud on-ramps helps even more. It shortens network paths and cuts the number of hops data has to take. Fewer hops mean lower latency and less variability.
Workload architecture matters too. Some applications tolerate minor latency variation, but others need highly synchronized systems across sites. In distributed environments, the distance between data centers affects replication speed, failover performance, and database consistency.
Look at data center location through user proximity, carrier access, and workload sensitivity. That keeps performance consistent as your infrastructure scales.
Geographic Proximity and Disaster Recovery
Geography is central to disaster recovery planning because a big event can hit a large area, including data centers. Floods, hurricanes, wildfires, grid failures, and large network outages can affect wide areas at once. If your primary and secondary data center locations sit too close together, one incident can knock out both. Geographic separation is the safer path because it reduces shared risk and strengthens business continuity planning. For that reason, strong disaster recovery strategies place backup infrastructure in a different seismic zone, power grid, or weather pattern. That lowers the odds that one natural disaster or utility failure takes both sites offline.
Distance also matters when you need to meet performance requirements. Replication between sites depends on network capacity and latency. Both show up in recovery time objectives (RTO) and recovery point objectives (RPO). You also need to assess regional hazard exposure, grid stability, and the strength of local telecommunications. Accessibility comes next, since teams may need physical access during long incidents.
Consider geography and data center location early in planning. Then it is easier to design disaster recovery environments that stay resilient and operationally stable.
Compliance and Security
Data residency and data sovereignty rules mean that the physical placement of infrastructure decides which national or regional laws apply. For example, healthcare organizations in the United States must follow HIPAA. Payment environments must meet PCI DSS standards, and organizations operating in Europe must comply with GDPR. These obligations follow jurisdiction. Laws apply based on where you store and process data, so location is a key factor in regulatory compliance.
Some countries enforce data localization laws that keep certain categories of information inside national borders. Check these laws when you choose a colocation provider. Cross-border data transfers can also trigger legal mechanisms, such as contractual safeguards and adequacy assessments.
Choosing a data center location can impact your organization’s entire compliance strategy. Certifications and independent audits show that facility controls meet recognized standards. But certifications alone cannot override jurisdictional rules. You still need to understand how local privacy laws affect storage, processing, and cross-region replication. Map your applications to the data they handle, review applicable regulations, and confirm your placement meets those requirements. That reduces legal exposure and simplifies audit preparation.
Expenses
Data center location has a direct effect on both capital and operating expenses. Placing infrastructure closer to primary users can reduce long-haul network transit, which lowers bandwidth and carrier costs over time. Shorter network paths also reduce the need for complex latency-mitigation strategies, like extra caching layers or distributed application nodes. Energy pricing is a major factor too. Electricity is one of the largest ongoing expenses for any data center, and rates vary widely by region. Locations with lower-cost power, or plenty of hydroelectric and other renewable sources, can save money in the long term. Cooler climates also help, because they allow better heat rejection and partial use of outside air for cooling. That reduces consumption.
Real estate, taxes, and labor markets also influence total cost. Cities have higher land and wage costs, whereas remote regions may need more investment in connectivity. Weighing these variables together helps your organization plan its finances for the long term.
User Experience
Data center location has a noticeable impact on user experience because distance affects how quickly applications respond. When infrastructure sits closer to the primary user base, data travels a shorter path. That lowers latency and improves page load times. The difference may only amount to milliseconds, but users feel it as smoother interactions and faster feedback.
For digital services such as e-commerce platforms, streaming media, SaaS tools, or online gaming, responsiveness directly influences user satisfaction. Higher latency can appear as longer buffering and delayed transactions, for instance. Over time, these friction points affect engagement and session duration.
Being close to major network exchanges also improves routing performance and reduces variability in response times. Consistent performance is important, especially for transaction-heavy or interactive applications. If your data center location matches where your users are, the experience becomes more predictable.
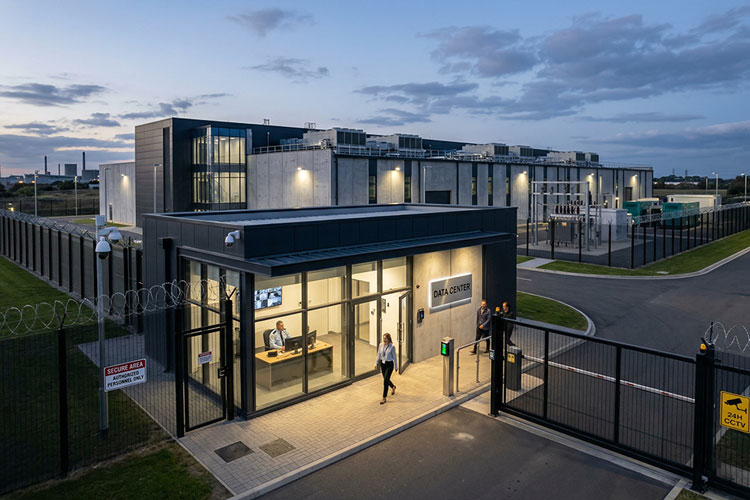
Data Center Security Must-Haves
Many factors matter when you evaluate a colocation provider, starting with whether it can handle your workload needs. Since you may be leaving your mission-critical data in the provider’s hands, security is a must-have.
Physical Security Measures
Physical security in a data center relies on layered controls. They restrict entry, monitor movement, and create a documented trail for investigations and compliance reviews. Policies and procedures matter, but data center location also influences how facilities put these controls in place. Facilities in higher-risk regions or dense city areas may need stricter perimeter security and more visible on-site presence. Industry best practice starts with continuous onsite staffing and active monitoring, including patrols and comprehensive CCTV coverage. The Uptime Institute names 24/7 staffing, structured visitor handling, and monitored surveillance as core elements of mature security.
Build access control around clearly defined secure zones that separate public or administrative areas from restricted technical spaces. Standards-based programs commonly use badge-and-PIN combinations or biometric authentication for higher-security areas. Documented authorization workflows drive access decisions. ISO/IEC 27001 Annex A emphasizes secure areas, entry controls, and visitor management as basic requirements. When these controls fit the chosen data center location, they create a defensible and auditable physical security framework.
Network Security
Logical security focuses on limiting what an attacker can access, even if they manage to compromise part of the environment. In a colocation model, you keep control over systems and configurations. The facility provides the surrounding connectivity between cages, sites, carriers, and cloud on-ramps as part of the secure architecture. Data center location can influence this design, especially when workloads span multiple regions or connect to specific cloud environments. A strong foundation begins with segmentation. Separate public-facing services, internal workloads, and management networks into defined zones, then enforce boundaries through firewalls and controlled interfaces.
This approach matches zero-trust principles. Applying least privilege reduces unnecessary exposure. You should also explicitly authorize east-west traffic between internal systems rather than trust it by default. CISA highlights microsegmentation as an effective way to limit lateral movement inside networks. Encryption should protect data in transit between facilities and cloud platforms, using properly configured TLS in line with NIST guidance. When logical controls fit your chosen data center location, secure connectivity becomes an embedded part of the facility’s resilience.
Compliance
Compliance-driven security gives you structured evidence that technical and operational controls work as intended. Recognized frameworks turn internal security practices into requirements that an independent party can verify. ISO/IEC 27001, for example, defines how to establish, maintain, and audit an information security management system (ISMS). SOC 1, SOC 2, and SOC 3 reports follow AICPA standards. They evaluate controls related to financial reporting and the Trust Services Criteria: security, availability, processing integrity, confidentiality, and privacy. PCI DSS governs payment card environments, while HIPAA sets safeguards for protected health information in the United States.
Data center location can influence how providers apply these requirements. This is especially true when jurisdictional rules or regional privacy laws affect where data may reside. Independent audits, run annually or on a defined cycle, provide formal proof that someone tested the controls. When you compare providers, confirm which certifications apply to each data center location. Also ask how often assessments happen and how they share reports under NDA.
Clear shared responsibility boundaries further improve compliance efforts. Mapping frameworks to where workloads operate makes it easier to show that controls are in place and working. Regular validation keeps them that way.
Planning for Capacity and Expansion
Scalability begins with a realistic view of how much room a market has to grow. In several major metros, new capacity sells out quickly. Utility availability has become one of the main constraints on expansion. When you evaluate data center location, look beyond current rack space. Ask whether the surrounding power grid, permitting process, and land supply can support higher-density deployments in the future. If your roadmap includes AI workloads, larger clusters, or bigger storage footprints, make sure the extra megawatts are truly available.
A thoughtful data center location strategy also has to consider how easily you can expand without forcing a redesign. Naturally, regions with established data center ecosystems offer easier expansion paths than markets with tighter constraints.
Hybrid Architecture and Workload Mobility
Most organizations now operate across multiple environments. They blend colocation, cloud, and on-prem systems into a broader hybrid IT infrastructure. In this context, data center location influences how efficiently those components connect and how flexibly workloads can move between them. Proximity to carrier-dense facilities and major cloud regions cuts latency variability and simplifies private connectivity.
Anchor services like identity platforms, shared storage, or connectivity hubs work best in the right data center location. There, they can support multiple environments without becoming a bottleneck. This flexibility makes it easier to adjust placement decisions over time.
Long-Term Constraints and Operational Risk
Scalability is also about minimizing future limitations that could become disruptive. Power demand continues to rise, and in some regions, utilities face increasing strain. The Uptime Institute has highlighted how growing energy consumption is reshaping planning priorities across the industry. In this environment, data center location becomes a risk management decision as much as a technical one.
Choose a data center location with stable utility infrastructure, realistic expansion timelines, and diversified connectivity. That reduces the chance of stalled projects. A geographically balanced footprint supports the evolution of hybrid IT infrastructure and keeps long-term scalability under control.
How Volico Data Centers Can Meet Your Needs
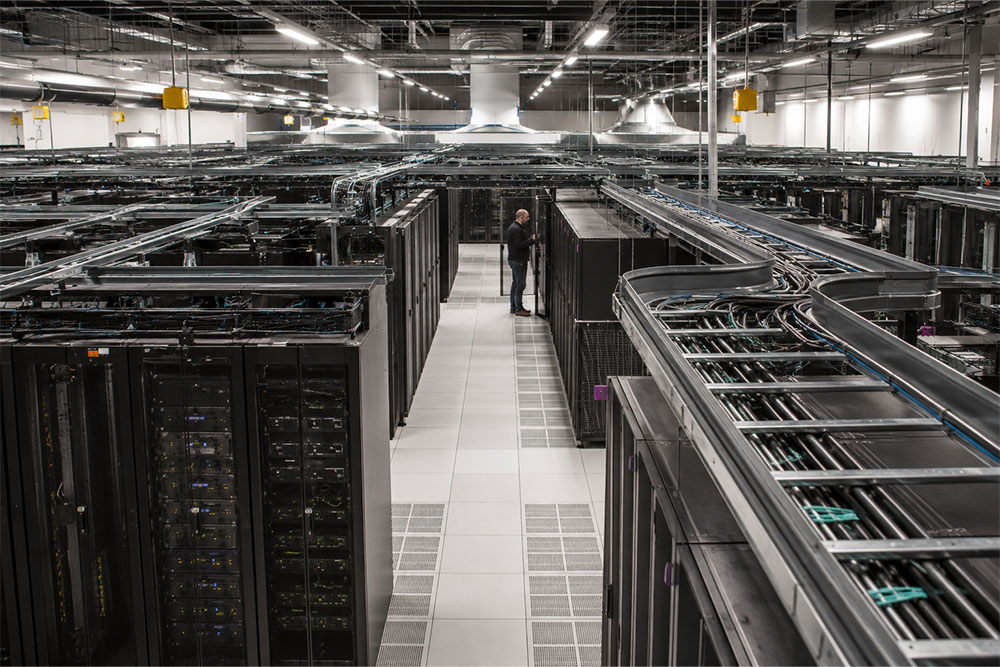
Volico Data Centers operates its facilities with multiple layers of physical and technical controls. These controls protect infrastructure and customer equipment. Our facilities feature redundant power and cooling systems that maintain availability and survivability under stress. A 24/7/365 Network Operations Center (NOC) watches infrastructure, connectivity, and application layer responsiveness in real time. Our certified technicians are always on duty to respond to events in accordance with service level agreements.
Volico maintains several compliance certifications that demonstrate adherence to widely recognized security standards:
- HIPAA
- SSAE16 / SOC 1 & SOC 2 Type II
- PCI DSS
- NIST compliance
Our data centers sit in major U.S. metro areas, including Miami, Fort Lauderdale, Atlanta, and Chicago. This helps reduce latency for users in those regions. Our facilities are carrier-neutral and offer strong interconnection capabilities. Customers get access to multiple telecommunications providers and cloud on-ramps that support performance and redundancy.
Miami is a strategically important data center location. The city serves as one of the primary network gateways between North America and Latin America. It has extensive subsea cable landings and major interconnection hubs such as the NAP of the Americas. This concentration of fiber infrastructure enables low-latency connectivity into key Latin American markets. It also gives strong access to U.S. backbone networks. Organizations serving customers across the Americas can remarkably reduce round-trip times by hosting in Miami instead of northern U.S. markets.
Carrier density and regional reach add to this advantage. Together, they support predictable performance for distributed and hybrid workloads across the U.S. and Latin America.
If you have any questions, contact us today, or schedule a tour.